4-day live training over Zoom
28 hours of intensive, hands-on training, with one year of access to every session recording for self-paced review.
Next live edition
Jun 7 – Jun 10, 2027
Sessions
4PM CET / 10AM EST
Registration closes
Jun 4, 2027
Learn to analyze, investigate, and respond to sophisticated malware and APT attacks, working hands-on with real-world samples from ransomware to APT toolkits. Amr Thabet.

Amr Thabet
CYBERSECURITY EXPERT · MALWARE RESEARCHER
Author of "Mastering Malware Analysis" book// Overview
Cyber attacks against government, military, public, and private organizations keep rising. Attackers want to steal valuable information, extort money through ransom, or damage reputations, and a large share of what organizations face today is advanced malware, APT activity, and zero-day attacks.
As adversaries get more sophisticated, detecting and responding to these intrusions has become a core skill for every security professional. The knowledge, skills, and tools needed to analyze malicious software are what let you detect, investigate, and defend against these attacks.
This training covers the entire incident response process, not just reverse engineering. You will move from static and behavioral analysis into assembly, IDA Pro, and debuggers, then tackle packed samples, encryption, and ransomware. On the final day you will bring it all together with Windows forensics, memory forensics with Volatility, and professional report writing.
The focus stays on the common, high-impact threats seen in the wild rather than theoretical or rare cases. Around 80% of the training is hands-on, using more than 100 real malware samples, from malicious documents and banking Trojans to modern ransomware and APT toolkits, all inside a safe lab environment.
// Training Benefits
28 hours of intensive, hands-on training, with one year of access to every session recording for self-paced review.
Start building the fundamentals right away with our Malware Incident Response Training course, available as soon as you enroll.
A digital copy of the book written by your instructor, the reference guide for malware analysts.
The Malware Incident Response VM, with over 100 pre-installed and configured tools, available for both VMware and Hyper-V.
// What You Will Learn
Day 1 sets the foundation with APT attacks and the full malware analysis workflow: static analysis, behavioral analysis, sandboxing, and malicious document analysis. You will work with real-world spear-phishing documents, examining VBA macros and malicious PDFs, and start extracting indicators of compromise from the first hour.
Day 2 takes you into code-level analysis. You will learn enough x86/x64 assembly to read malware in IDA Pro and x64dbg, then apply it immediately to real samples, analyzing droppers, keyloggers, banking Trojans, and packed malware. You will also write your first YARA rules to detect what you find.
Day 3 is about the hard problems: encryption and ransomware. You will reverse basic and complex encryption algorithms (RC4, AES, public key), uncover encrypted strings and C2 domains, and analyze real ransomware samples to assess whether decryption is possible.
Day 4 brings it all together with Windows forensics, memory forensics using the Volatility framework, and professional report writing. You will analyze a Stuxnet memory dump, detect process hollowing and injected DLLs, build attack timelines, and write a report that answers the questions management asks during an incident.
// Full Syllabus
// Target Audience
Professionals who investigate incidents and threats and need advanced skills in malware analysis and incident handling.
Security leaders who need to understand advanced threats, build response strategies, and guide their teams during malware incidents.
SOC analysts, incident responders, and threat hunters who want to get better at analyzing and responding to advanced malware incidents.
// Prerequisites
// Takeaways
Learn the strategies, tactics, and techniques to respond to malware and ransomware attacks in enterprise environments, with a structured approach from identification to containment.
Perform professional malware analysis to extract indicators of compromise, understand malware capabilities, and disrupt attacker communication channels.
Conduct digital and memory forensics, build effective containment plans, and communicate findings to management with technical precision.
// Training Structure
Every topic is taught with a real sample. You will not analyze toy binaries. The exercises use the same malware that organizations encounter in actual incidents. The lab environment comes with over 100 pre-installed tools and more than 100 real malware samples ready to analyze.
The training is cumulative. Each day builds on the previous one, so by day 4 you can take a sample you have never seen before, analyze it from static analysis through code analysis, deal with its encryption, and produce a professional report with timelines and IoCs.
// Your Trainers
 Lead
CYBERSECURITY EXPERT · MALWARE RESEARCHER
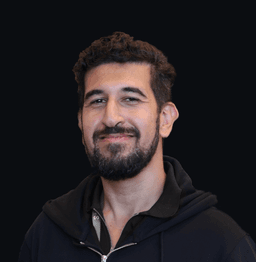
Amr Thabet is a cybersecurity expert with 12+ years of experience in malware research and incident handling. He has worked with Fortune 500 companies worldwide and is the author of "Mastering Malware Analysis". Amr specialises in advanced malware hunting, digital forensics, threat hunting, and Windows internals security.
// ROI for Your Organization
Your team learns to extract IoCs, understand what a sample does, and contain it without waiting on an outside vendor in the middle of an incident.
Analysts learn to write professional malware analysis reports and answer the business questions leadership asks during a ransomware or APT incident.
The analysis VM, report templates, YARA templates, and the instructor's book stay with your team long after the four days are over.
// Pricing
Early Bird
$1,260
Ends Apr 26
Regular
$1,800
Ends Jun 4
4 days of live, instructor-led training over Zoom (28 hours)
Certificate of completion
1-year access to all session recordings
Access to a cloud-based lab environment for the duration of the training
Training slides
Exercise workbook with all exercises and step-by-step solutions
Instant access to the Malware Incident Response Training bonus course
Digital copy of Mastering Malware Analysis, 2nd Edition
Malware Incident Response VM with 100+ pre-installed tools (VMware and Hyper-V)
Real-world malware samples, source code, and analysis tools
Custom YARA rule templates and cheat sheets
Professional malware analysis report templates
Post-training support and community access
All prices net, VAT excl.
// Register · June 7 · 4PM CET
4 days · 14 modules · live and hands-on with Amr Thabet. Limited to 30 participants.
All prices net, VAT excl.
$1,800$1,260 net · All prices net, VAT excl.
// Register · June 7 · 4PM CET
4 days · 14 modules · live and hands-on with Amr Thabet. Limited to 30 participants.
$1,800 $1,260
All prices net, VAT excl.
// Pricing
Early Bird
$1,260
Ends Apr 26
Regular
$1,800
Ends Jun 4
4 days of live, instructor-led training over Zoom (28 hours)
Certificate of completion
1-year access to all session recordings
Access to a cloud-based lab environment for the duration of the training
Training slides
Exercise workbook with all exercises and step-by-step solutions
Instant access to the Malware Incident Response Training bonus course
Digital copy of Mastering Malware Analysis, 2nd Edition
Malware Incident Response VM with 100+ pre-installed tools (VMware and Hyper-V)
Real-world malware samples, source code, and analysis tools
Custom YARA rule templates and cheat sheets
Professional malware analysis report templates
Post-training support and community access
All prices net, VAT excl.
