4-day live training over Zoom
28 hours of intensive, hands-on training, with one year of access to every session recording for self-paced review.
Next live edition
Sep 20 – Sep 23, 2027
Sessions
4PM CET / 10AM EST
Registration closes
Sep 17, 2027
An advanced, hands-on red team program on emulating real adversaries, building custom offensive tooling, and testing defenses so organizations can strengthen them. Amr Thabet.

Amr Thabet
CYBERSECURITY EXPERT · MALWARE RESEARCHER
Author of "Mastering Malware Analysis" book// Overview
Organizations face increasingly sophisticated targeted attacks and ransomware. To improve their security posture, teams need to be able to emulate real adversaries and put their defensive capabilities to a genuine test.
This hands-on training focuses on the tradecraft behind advanced targeted attacks and how defenders can measure and improve their resilience against it. You will study how modern campaigns are built and operated, and practice the same techniques inside a controlled, cloud-based lab so that every lesson maps back to a defensive takeaway.
Across four days you will stand up red team infrastructure on AWS with Terraform and Caldera, work through phishing and initial access, develop custom tooling, and study evasion, credential access, and lateral movement, all mapped to the MITRE ATT&CK framework. The emphasis is on understanding how each technique works so you can detect and defend against it.
This is an advanced course. It assumes a solid Windows and cybersecurity background and comfortable C++ programming skills, and everything is taught strictly for authorized testing and defensive improvement.
// Training Benefits
28 hours of intensive, hands-on training, with one year of access to every session recording for self-paced review.
Complete Terraform templates and documentation for building secure red team infrastructure in AWS.
Full source code for every tool and framework developed during the training, including the C2 infrastructure.
A pre-configured virtual machine with all the required development and testing tools, ready to use from day one.
// What You Will Learn
Day 1 starts with real APT attack analysis and infrastructure deployment. You will set up a full red team environment in AWS using Terraform, deploy Caldera as your C2, and then work through phishing and initial access: building phishing pages with GoPhish and Evilginx2, bypassing two-factor authentication, and executing spear-phishing attacks with malicious documents, LNK files, and COM objects.
Day 2 is about building your own tools. You will develop a custom HTTP implant in C++ that communicates with Caldera, implement a plugin framework, build persistence mechanisms, and develop privilege escalation techniques including UAC bypasses and service-based escalation to SYSTEM.
Day 3 covers the evasion techniques that make the difference between getting caught and staying in. You will implement string encryption, dynamic API loading, steganography, and anti-analysis methods. On the network side, you will build HTML smuggling, HTTPS communication, and DNS/ICMP channels. The day closes with EDR bypass techniques: process injection, API unhooking, invisible injection, and AppLocker bypasses.
Day 4 focuses on credential access and lateral movement, the final stages of a real engagement. You will dump LSASS, impersonate tokens, hijack RDP sessions, and implement the full Kerberos attack chain: Pass-the-Hash, Golden Ticket, and domain takeover. The module closes with automating lateral movement across an enterprise.
// Full Syllabus
// Target Audience
Cybersecurity professionals who want to expand their offensive security skills and understand advanced attack techniques.
Pentesters who want to level up with custom tool development and advanced evasion techniques.
Red teamers who want to strengthen their technical capabilities and learn professional infrastructure deployment.
// Prerequisites
// Takeaways
Simulate real APT attacks by understanding and reproducing their TTPs in a controlled environment, so you can test and improve an organization's security posture.
Develop your own offensive security tools instead of relying only on off-the-shelf ones, and gain a deep technical understanding of how attack tools work.
Deploy and manage professional red team infrastructure on modern cloud platforms, with the operational security practices real engagements demand.
// Training Structure
Everything is implementation-first. You will not just learn what a technique does, you will write the code that does it. Every tool and framework you use during the training is something you build yourself, and you leave with the full source code.
The training maps every technique to the MITRE ATT&CK framework, so every attack you build comes with the context of where it fits in a real campaign and how defenders can detect it. This is an offensive course taught with a defensive mindset.
// Your Trainers
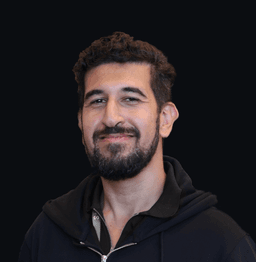 Lead
CYBERSECURITY EXPERT · MALWARE RESEARCHER
Amr Thabet is a cybersecurity expert with 12+ years of experience in malware research and incident handling. He has worked with Fortune 500 companies worldwide and is the author of "Mastering Malware Analysis". Amr specialises in advanced malware hunting, digital forensics, threat hunting, and Windows internals security.
// ROI for Your Organization
Your team learns to emulate the TTPs behind real APT and ransomware campaigns, giving you a realistic measure of how your controls hold up.
Operators learn where modern defenses succeed and where they fall short, turning each engagement into concrete detection and hardening work for the blue team.
Instead of outsourcing every red team engagement, your staff come away able to run professional, cloud-based operations with tooling they understand end to end.
// Pricing
Early Bird
$1,800
Ends Aug 9
Regular
$2,400
Ends Sep 17
4 days of live, instructor-led training over Zoom (28 hours)
Certificate of completion
1-year access to all session recordings
Access to a cloud-based lab environment for the duration of the training
Training slides
Exercise workbook with all exercises and step-by-step solutions
AWS infrastructure Terraform templates and documentation
Full source code for all tools and frameworks built in the training
Pre-configured development virtual machine
Infrastructure deployment guides and tool development templates
Post-training support access
All prices net, VAT excl.
// Register · September 20 · 4PM CET
4 days · 12 modules · live and hands-on with Amr Thabet. Limited to 30 participants.
All prices net, VAT excl.
$2,400$1,800 net · All prices net, VAT excl.
// Register · September 20 · 4PM CET
4 days · 12 modules · live and hands-on with Amr Thabet. Limited to 30 participants.
$2,400 $1,800
All prices net, VAT excl.
// Pricing
Early Bird
$1,800
Ends Aug 9
Regular
$2,400
Ends Sep 17
4 days of live, instructor-led training over Zoom (28 hours)
Certificate of completion
1-year access to all session recordings
Access to a cloud-based lab environment for the duration of the training
Training slides
Exercise workbook with all exercises and step-by-step solutions
AWS infrastructure Terraform templates and documentation
Full source code for all tools and frameworks built in the training
Pre-configured development virtual machine
Infrastructure deployment guides and tool development templates
Post-training support access
All prices net, VAT excl.
